Cybersecurity is a marathon runner's discipline. Between recon, enumeration, and exploitation, there comes a point where your brain saturates. I learned a fundamental lesson: knowing when to stop so you can come back stronger.
Here's a summary of the wins and lessons from this productive day.
🎯 The day's wins
Despite the difficulty of certain points, this day was rich in "quick wins" and skill consolidation:
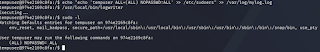
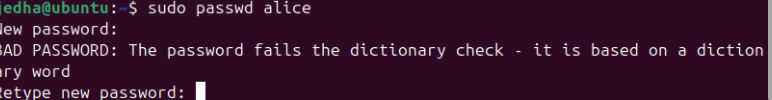
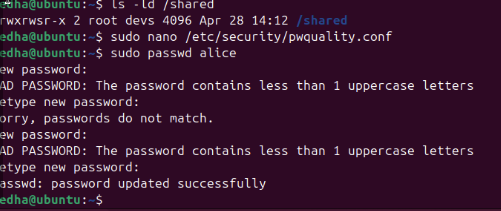
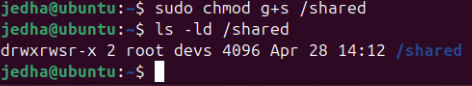
Folder sharing: An efficient exploration of attack vectors on this service. I was able to confirm the attack surface was limited, which let me quickly isolate potential flaws.
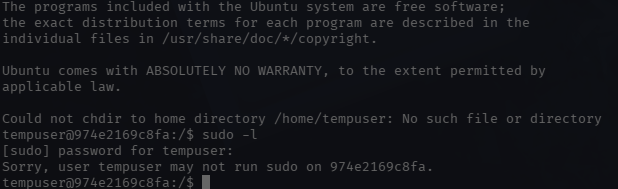
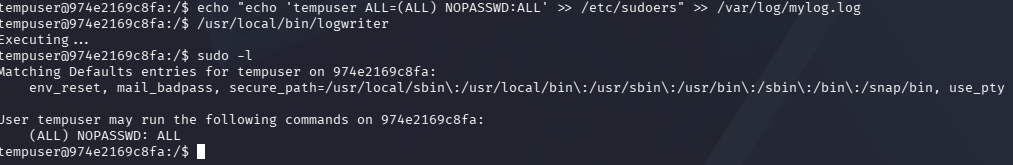
Exploiting misconfigurations: An exercise focused on [Theme: e.g. network enumeration / automated scripts]. What struck me was the need to properly structure your commands so as not to drown in system noise.
🧠 Lessons learned
Beyond the pure technical side, this day reminded me of three essential truths for any aspiring hacker:
Methodology beats tooling: I tend to want to test every possible exploit, but a methodical, step-by-step approach avoids burning out on dead ends.
The importance of documentation: Taking notes in real time, even on leads that fail, keeps you from retracing the same path twice.
Rest is part of the training: The brain keeps processing complex problems in the background. The solution to what's blocking me now will probably seem obvious after a night's sleep.